Resources & insights

Practical guidance for buyers and IT leaders.

Buying guides, security best practices, and decision frameworks written by the engineers and account managers who do this work every day. No hype, just what we would tell a client across the table.

Buying guide

How to plan a business laptop refresh

By the GoldenTech KSA procurement team · 8 min read

A laptop refresh is one of the most visible IT projects a business runs. Done well, it lifts productivity and closes security gaps in a single cycle. Done badly, it creates weeks of disruption and a pile of unused equipment. This guide walks through the decisions that matter, in the order you should make them.

1. Decide when, not just whether

Most business laptops deliver good value for three to four years. Beyond that, battery degradation, slower performance, and the end of manufacturer warranty combine to raise support costs faster than the device's remaining value falls. Pull the age and warranty expiry of every device from your asset inventory, and group them into refresh waves rather than replacing everything at once. Staggering the fleet smooths both cash flow and support workload, and it means you are never facing a hundred simultaneous end-of-life dates again.

2. Define two or three specification tiers

Resist the urge to spec a single "standard" laptop. Roles differ, and over-buying for administrative staff is as wasteful as under-buying for engineers. A practical split is a standard tier for office and administrative roles, a performance tier for users running heavy applications or many browser tabs and video calls, and, where needed, a mobile tier that prioritizes weight and battery life for field staff. Keep the tiers to the same vendor family where possible, so drivers, docks, and spare parts are interchangeable.

3. Standardize the peripherals

Docking stations, monitors, and headsets often account for a quarter of a refresh budget and most of the help-desk noise afterwards. Choose one dock model that works across all your tiers, confirm it supports the monitor resolutions you actually run, and buy a few spares. If your staff work from home, decide now whether the company supplies a second dock and monitor or offers a stipend.

4. Plan imaging and deployment before ordering

A device that arrives without being configured is a support ticket waiting to happen. Modern deployment tools let a supplier enrol devices into your management platform before shipment, so they arrive with your policies, applications, and security baseline already applied. Ask your supplier whether they offer staging, asset tagging, and drop-shipping to individual users, and whether those services are priced per unit or bundled. For larger fleets, a pilot group of ten to twenty users will surface application or driver problems before the main wave.

5. Budget for the whole lifecycle

The unit price is rarely the whole cost. Add extended warranty or accidental-damage cover where devices travel, the labour to deploy and migrate data, licensing for any new operating system or management tools, and the secure wiping and disposal or resale of the outgoing fleet. A simple total-cost-of-ownership sheet per tier makes it easy to compare supplier quotes fairly and to defend the budget internally.

6. Communicate and schedule

Tell users what is changing, when, and what they need to do, usually a data check and a backup of anything stored locally. Schedule swaps around the business calendar, avoiding month-end for finance and peak season for operations. Keep a small buffer of configured devices for new starters and failures so the refresh does not collapse into ad-hoc purchasing afterwards.

A refresh planned this way typically takes six to ten weeks from specification to the last swap, with minimal disruption. The decisions in this guide are exactly the ones we work through with clients when scoping a fleet order.

Related service: Procurement & fulfillment: staged, imaged laptop deployments at wholesale pricing

Best practices

A 12-point cybersecurity checklist for SMBs

By the GoldenTech KSA security team · 6 min read

Most successful attacks on small and mid-sized businesses are not sophisticated. They exploit a missing patch, a reused password, or a backup that was never tested. The twelve controls below address the overwhelming majority of real-world incidents we see, and they are listed in the order we recommend implementing them. None requires an enterprise budget; all of them require someone to own them.

  1. Enforce multi-factor authentication everywhere. Start with email, remote access, and any administrative account. Stolen passwords are the single most common entry point, and MFA neutralizes most of them.
  2. Patch operating systems and applications within days, not months. Automate updates for workstations and schedule a monthly maintenance window for servers and network devices, with emergency patching for actively exploited vulnerabilities.
  3. Deploy managed endpoint detection and response. Traditional antivirus is no longer enough; modern endpoint protection detects behaviour, isolates compromised machines, and alerts someone who will act on it.
  4. Back up critical data and test restoring it. Keep at least one copy offline or immutable so ransomware cannot encrypt it, and run a restore test quarterly to confirm the recovery time is acceptable.
  5. Remove local administrator rights from everyday users. Most malware needs elevated privileges to do real damage; standard user accounts stop it cold and cost nothing.
  6. Filter email for phishing and malicious attachments. Layer a reputable email security service on top of your mail platform, and configure SPF, DKIM, and DMARC so your own domain cannot be easily spoofed.
  7. Train staff and run simulated phishing. Short, regular training paired with realistic test emails measurably reduces click rates within a few months.
  8. Segment the network and secure the perimeter. Put guest Wi-Fi, printers, cameras, and other devices on separate networks from workstations and servers, behind a business-grade firewall with current firmware.
  9. Encrypt laptops and mobile devices. Full-disk encryption turns a lost laptop from a data-breach notification into a hardware replacement.
  10. Maintain an accurate asset and account inventory. You cannot protect what you do not know about; review devices and user accounts quarterly and remove anything that has left the business.
  11. Centralize logging and review alerts. Collect logs from firewalls, servers, and identity systems in one place, and make sure alerts reach a person or provider who will investigate them.
  12. Write and rehearse an incident response plan. A one-page plan naming who to call, what to isolate, and how to communicate turns a chaotic day into a managed one.

If you work in a regulated sector, these controls also map closely to the baseline requirements of most compliance frameworks and cyber-insurance questionnaires. Score your organization honestly against each point, then fix the gaps from the top of the list down. The order matters more than the pace.

Related service: Cybersecurity & compliance: assessments, managed protection, and remediation

Comparison

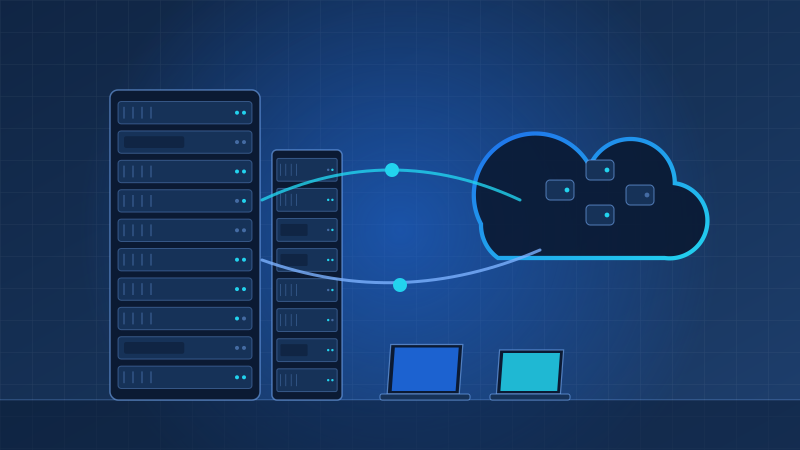
Cloud, on-premises, or hybrid?

By the GoldenTech KSA infrastructure team · 7 min read

"Should we move to the cloud?" is the wrong question, because the answer is almost never all-or-nothing. The useful question is where should each workload live, and the answer depends on cost, performance, compliance, and how much operational effort you want to own. This is the framework we use with clients.

Start with an inventory of workloads

List every system the business relies on: email and collaboration, file storage, line-of-business applications, databases, backups, and any specialist equipment such as manufacturing controllers or imaging systems. For each, note who uses it, how sensitive the data is, how much it would hurt to lose it for a day, and whether the vendor even supports running it in the cloud. Many placement decisions become obvious at this stage.

Where cloud usually wins

Commodity services such as email, calendars, document collaboration, video calls, and identity are almost always better delivered as cloud subscriptions. The vendor handles patching, redundancy, and scale, and the per-user cost is predictable. Workloads with variable demand, remote users spread across regions, or a need for rapid provisioning also favour public cloud. If your current server room exists mainly to host email and files, the case for moving is strong.

Where on-premises still makes sense

Applications with heavy, steady compute or storage requirements can cost significantly more in the cloud over a five-year horizon than well-sized hardware you own. Systems tied to physical equipment, latency-sensitive workloads, and sites with unreliable internet connectivity also argue for local infrastructure. Some regulatory regimes and client contracts require data to remain in a specific location or under direct control. In these cases a modern, properly supported on-premises environment is not a legacy choice. It is the right one.

Hybrid: the realistic default

For most organizations the outcome is hybrid: cloud for collaboration and elastic workloads, local infrastructure for the systems that need it, and a consistent identity, security, and backup layer spanning both. The risk with hybrid is complexity: two environments to secure and manage. Mitigate it by standardizing on one identity provider, one backup platform that covers both locations, and one monitoring view.

Model the real cost

Compare a five-year total cost for each option, not a monthly subscription against a hardware invoice. Include licensing, support contracts, power and cooling, staff time, internet bandwidth upgrades, and the eventual hardware refresh. Cloud egress and storage growth are commonly underestimated; hardware support and downtime costs are commonly ignored. An honest model often shows that the cheapest answer differs by workload, which is precisely why the question should be asked per workload.

Sequence the change

Move the easy, low-risk services first, learn from them, and revisit the harder decisions with real data. Keep the old environment running in parallel until each cutover is proven, and document the end state so the next person can understand why things live where they do.

Related service: Cloud & infrastructure: assessments, migrations, and hybrid environments

Stay informed

Guides, security advisories, and availability updates

One email a month with new articles, notable security advisories affecting business systems, and product availability or pricing changes worth knowing about. No spam, and unsubscribe at any time.

Subscribe to the newsletter

By subscribing you accept our Privacy Policy.

Want this advice applied to your environment?

Our engineers turn these frameworks into scoped, priced plans for a laptop refresh, a security programme, or a cloud decision.